Mongolian broadband provider Mobinet is deploying Plume Design’s Plume Platform to power its mobihome broadband service.
The agreement will provide Mobinet customers with access to AI-optimised Wi-Fi, advanced cybersecurity protection, parental controls and real-time home network management through an intuitive mobile app. The Plume Platform continuously learns and adapts to each household, helping deliver stronger Wi-Fi coverage, more reliable connectivity and a safer online experience.
Bat-Erdene Tuvd, Chief Technology Officer of Mobinet, said that the deal would provide its customers with “better Wi-Fi, stronger security and greater control” of their online activities, as well as “faster support and a better overall customer experience without increasing costs.”
As part of its commitment to customer satisfaction, Mobinet is introducing these advanced capabilities to subscribers without additional monthly charges. The Plume Platform enables faster and more proactive customer support via greater visibility into home network performance, allowing Mobinet to identify and resolve many issues remotely, reducing service interruptions, minimizing technician visits and ensuring smoother complaint handling.
“Mobinet understands that customer experience is the true differentiator in today’s broadband market,” said Chris Griffiths, Chief Technology Officer of Plume. “Mobinet selected the Plume Platform because of its unique ability to deliver smarter, safer and more reliable connectivity to households across Mongolia in a single unified solution.”
The Connected Britain Awards winners have been announced, following a highly successful Connected Britain conference
With a record-breaking number of entries this year, the Connected Britain Awards 2026 showcased the most innovative and exciting elements of Britain’s ever-growing and rapidly evolving digital economy. This year’sshortlist included a fantastic array of diverse organisations and individuals, all of whom were highly deserving of praise.
A big thanks to all our award presenters and to our expert panel of judges for lending us their expertise in selecting the winners.
Access Innovation Award
For this category the judges were looking for an entry that did something special to help deliver connectivity to a previously hard-to-reach location.
The winning entry created a system that did exactly this, drastically cutting installation time, costs, and waste, finally making broadband delivery economically viable for many rural locations in the UK.
Emtelle – Rapid Customer Connect
Indoor Connectivity Award
The winner in this category pulled off a remarkable engineering feat, delivering high‑capacity 4G and 5G coverage at three locations, positively impacting millions of users.
Wireless Infrastructure Group
Customer Champion Award
Combining proactive network management with outstanding local support, this entry demonstrated a true customer-first philosophy backed by exceptional satisfaction and retention scores.
Lightning Fibre
Highly commended: 4th utility Rise
Barrier Removal Award
This entry delivered a masterclass in collaboration and leadership by creating an open-access framework to simplify asset access, lower deployment costs, and accelerate fiber rollout.
West Sussex County Council for OpenAccess West Sussex
Startup of the Year
ZIM Connections
Sustainability Award
Challenging the throwaway culture of tech, the winning entry in this category sought to prevent e-waste through high-quality engineering and prioritizing ‘longevity by design’.
FRITZ! & Zen
Mobile Service Provider of the Year
The winner in this category demonstrated a European first, deploying exciting new network capabilities that could reshape the approach to mobile connectivity across the UK.
Virgin Media O2 – O2 Satellite
Highly commended: VodafoneThree
AI Innovation Award
Turning back-office audits into live, real-time field support, the winning solution slashed telecom fault rates by up to 50% within 60 days and set a new benchmark for AI operational value.
SkillsBase Forge
Highly Commended: Zyxel One powered by Lifemote
Data Centre Project of the Year
This winning project delivered a resilient, sustainable data centre transformation, notably making use of waste heat to benefit a local campus.
Advanced Power Technology and Schneider Electric
Broadband Provider Award
Proving that mastering the basics drives extraordinary results, this provider achieved an outstanding NPS, near-zero churn, and market differentiation through early Wi-Fi 7 rollouts.
Connect Fibre
Highly commended: Fibrus
Enterprise Solution Award
This team introduced a transformational solution that addresses complex enterprise connectivity challenges while delivering clear operational flexibility.
The winner here is potentially the landmark deal of the decade in UK connectivity, structured to unlock massive long-term investment, competitive scale, and enhanced connectivity across the nation.
VodafoneThree
Infrastructure Builder of the Year
Using a holistic approach to network deployment, this specialist delivered a Project Gigabit contact ahead of schedule working in one of the UK’s most challenging environments.
Viberoptix
Digital Skills Award
For this entry, the judging panel was highly impressed by a targeted, scalable digital skills initiative that directly tackles digital exclusion and builds long-term confidence across local communities.
Norfolk County Council – Tech Skills for Life and Digital Skills Team
Highly Commended: Kent County Council, Medway Council and East Kent College Group
Public Sector Partner Award
This award celebrates a private company that has done exceptional work in partnership with public sector organization.
The winning partnership deployed IoT at scale, showing a high level of cooperation and effectively shifting property maintenance from reactive to predictive, potentially having a major impact on residents’ health.
iOpt & ng homes
Public Sector Trailblazer Award
While the previous award celebrated those working with the public sector, this award goes to a public organization itself.
This entry overcame tough engineering hurdles to add an additional layer of connectivity to services, positively impacting thousands of users every day. We hope to see similar initiatives repeated across the country.
Scotrail for their Starlink satellite integration
Highly commended: The Scottish Government
Rising Star Award
The judges were blown away by this individual’s early-career leadership, with one judge saying: ‘These achievements are exceptional for any age, and remarkable for such an early career stage.”
The winner has already led major fibre deployment projects and delivered remarkable infrastructure impact well beyond their years.
Cameron Moir, GoFibre
Highly commended: Emily Jones, TTB CircularIT & Harry Turfrey, CityFibre
OSS/BSS Innovation of the Year
A standout story in network automation, this entry leveraged an AI-powered digital twin to deliver massive efficiency benefits, both in network deployment and ongoing operations.
Virgin Media O2 – Challenger OSS
Community Improvement Award
This inspiring project stood out for tackling a major challenge facing our industry and society at large: nurturing the next generation of STEM professionals. This initiative focused not only on educating, but on empowering underserved local communities with transformative technology skills beyond the basic curriculum.
The LuLu Coastal Cable System the Kenyan coast’s first fully protected coastal cable system, has been announced at this week’s ITW Africa digital infrastructure and connectivity event, held in Nairobi.
LuLu is a submarine cable designed to strengthen connectivity along Kenya’s 500 kilometre Indian Ocean coast, linking five strategic landing points from Mombasa to Lamu, including Vipingo Special Economic Zone (SEZ), Kilifi and Malindi.
It is an integrated system combining a submarine cable running along the Indian Ocean seabed with a parallel, protected terrestrial pathway. The developers of the system say that this dual-path protection architecture – submarine and terrestrial running in parallel – delivers the levels of resilience that international cable systems, data centre operators, and enterprise customers require as a baseline operating condition.
It is to be co-developed by INDOI (IOX), a Mauritius-headquartered ICT infrastructure developer, Blue Trade Investments Limited, a Kenyan investment company, ARISE Integrated Industrial Platforms, which designs, finances, conceives and operates industrial ecosystems across Africa, advisory company AfriTrade Consulting Group, and Kingdom Bank, a subsidiary of the Co-operative Bank of Kenya.
The system will use DWDM technology in the 1550nm window, with 144 fibre pairs and a design capacity of up to 60 Tbps per fibre pair. It is designed for a 25-year operational life, with centralised network management, and is expected to be ready for service in Q2 2028, subject to contract execution.
Blue Trade, INDOI’s Kenya-registered infrastructure partner, is the designated cable landing party, regulatory interface, and operational delivery partner for LuLu in Kenya. Blue Trade says its established relationships with Kenya’s regulatory authorities, coastal communities, and government institutions provide the critical local foundation upon which INDOI’s regional infrastructure vision is built and sustained.
The LuLu landing at Vipingo SEZ is described as the catalyst for a broader transformation. The partners say that direct submarine cable connectivity within the SEZ boundary unlocks investment categories that manufacturing infrastructure alone cannot attract: hyperscale data centres, cloud service provider regional nodes, fintech and payment processing platforms, cybersecurity operations centres, and IoT-driven smart manufacturing services, to name only a few.
LuLu’s Mombasa landing will connect the entire coastal system to the global internet backbone from day one giving every LuLu landing station, and every tenant and operator these stations serve, seamless access to existing submarine cables landed in Mombasa and beyond.
As news service SubTel Forum notes, however, the information so far released does not name a system supplier, construction start, route-survey schedule or completed contracts.
Huawei is positioning wearable technology as more than a consumer electronics category, increasingly using its wearable devices as platforms for health monitoring, data collection and medical research.
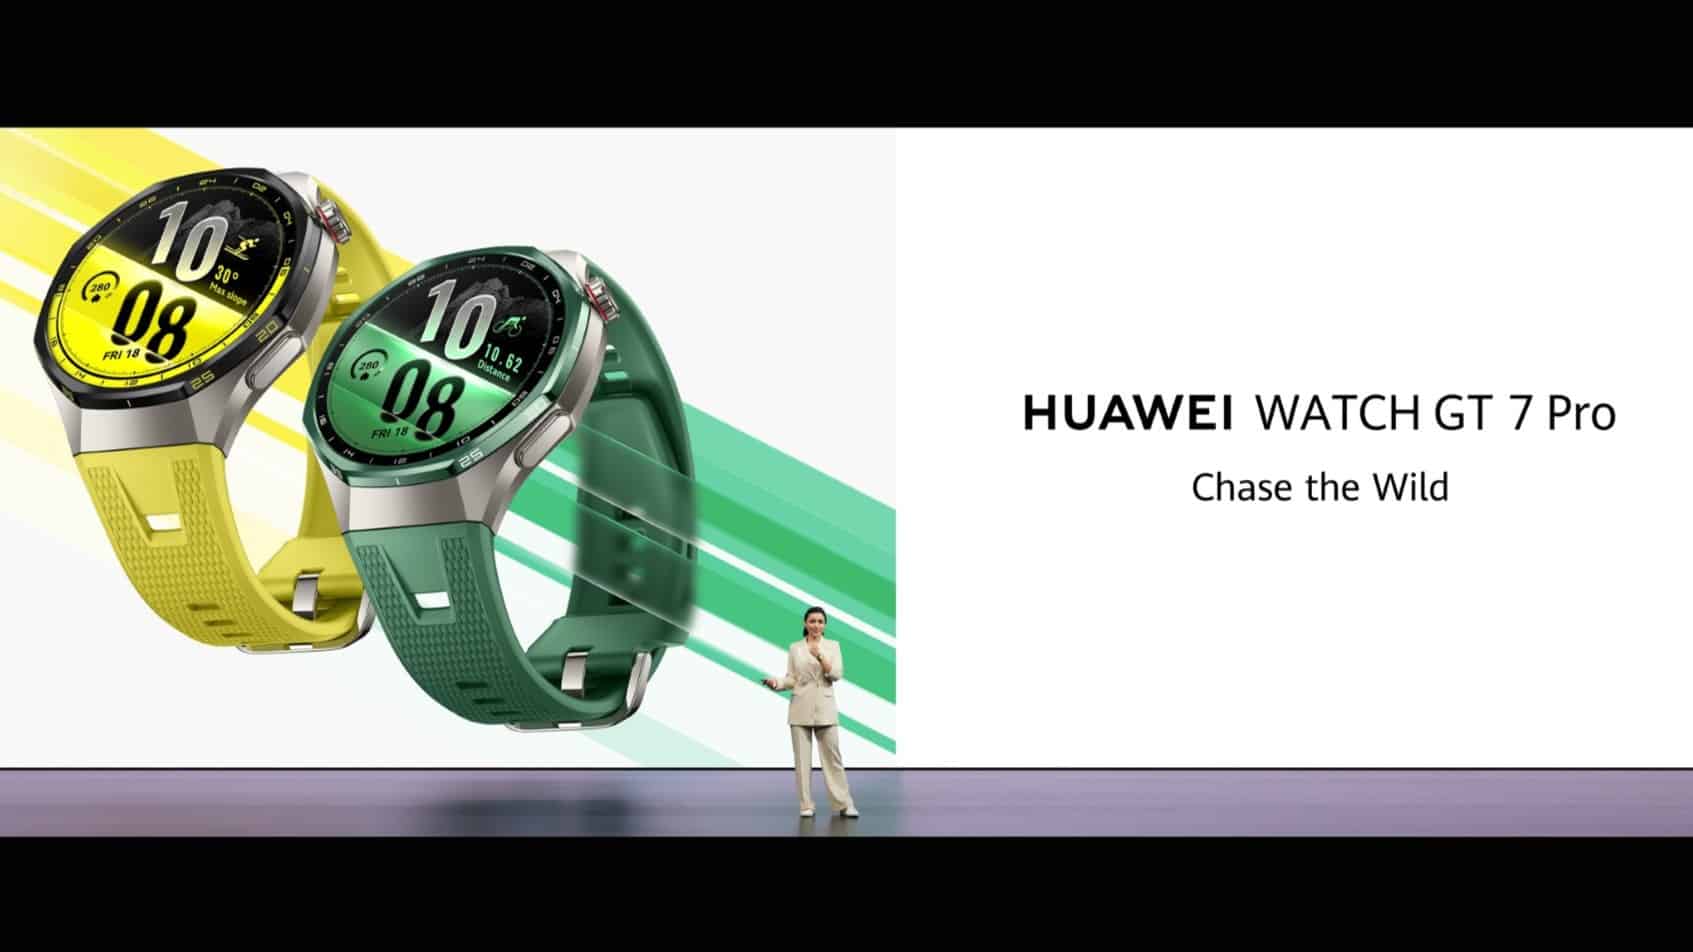
The strategy was on display at SHOWPALAST in Munich, Germany, where Huawei showcased the Watch D3 and its European Terve Research platform alongside its broader smartwatch portfolio. Huawei’s products captured the event’s ‘Chase the Wild’ theme as the products are designed to help users track their activities and use the data to better manage their health and lifestyle.
Watch D3 combines advances in blood pressure monitoring, while Terve is a European research platform designed to connect wearable-generated data with academic and medical research. The Watch D3 launched globally on September 2, while Terve Research is being introduced as an infrastructure layer for European medical and academic institutions.
The move comes as health tracking becomes an increasingly crucial element for smartwatch and wearable manufacturers. Market research firm Counterpoint Research now tracks features such as sleep apnea detection, ECG and blood pressure monitoring alongside shipments, revenue and average selling prices in its global smartwatch market analysis.
“From metabolic monitoring and active health management to brain activity sensing, wearables are no longer just about your wrist. We are moving toward a complete picture of your health, a full-body system that monitors, understands, and responds,” said Rico Zhang, President of Huawei’s Smart Wearable and Health Product Line.
While the technology is advancing rapidly, there have been questions raised around validation, calibration and performance of wearable health monitoring tools. In this context, Huawei’s approach is particularly notable because Watch D3 combines conventional oscillometric measurement using a miniature pump and airbag with Photoplethysmography (PPG)-based continuous trend monitoring, rather than relying exclusively on cuffless estimation.
From smartwatch to health platform
Significantly, Huawei has been building toward this position for several years. The first-generation Watch D introduced wrist-based blood pressure measurement in 2021, while the Watch D2 added 24-hour Ambulatory Blood Pressure Monitoring (ABPM) in 2024. The D3 takes the concept further by attempting to reduce one of the principal drawbacks of ABPM: the disruption caused by repeated cuff inflation.
The watch uses four high-precision micro-pump measurements during the day and three at night, while PPG continuously tracks blood-pressure trends between those measurements. Huawei describes this as a “precision measurement plus trend tracking” approach, intended to retain reliable measurements while reducing the frequency of disruptive inflations.
The device has received CE Medical Device certification for resting blood pressure measurement, ABPM and pre- and post-exercise blood pressure monitoring. Huawei claims it is the world’s first wrist-worn device to pass ISO standards for accurate blood-pressure measurement before and after any physical activity, to help users in building sustainable fitness habits.
Huawei’s focus on measurement methodology gives Watch D3 a differentiated position in an increasingly crowded health-wearable market. Watch D3 is 17.7% thinner and 9% lighter than its previous version, making it easier for the user to wear and benefit from the device.
Building an ecosystem around the wrist
The larger opportunity for Huawei, however, may extend beyond the device itself. Terve Research is designed as an online platform through which European academic and medical institutions can conduct wearable-based studies as well as recruit participants. Funded by Huawei but independently managed and operated by medical technology provider Thryve, the platform allows researchers to conduct closed studies with selected participants or open studies involving eligible Huawei wearable users who voluntarily opt in.
The platform is launching with two studies: one examining the health impact of social jetlag and disrupted circadian rhythms, and another investigating the relationship between exercise patterns and cardiovascular risk. Both are being led by European medical researchers and use data collected from Huawei wearable devices.
This creates a potentially valuable feedback loop: wearables generate real-world data, researchers use that data to investigate health patterns, and those findings can help in the development of future products and health services.
It is also a direction that reflects the broader evolution of the wearable market. The industry is gradually moving away from counting steps and monitoring basic fitness metrics toward continuous health monitoring, preventive care and research applications.
From consumer electronics to digital health
Huawei also announced the launch of is also expanding its smartwatch portfolio with the HUAWEI WATCH GT 7 Series, which brings upgrades across sports tracking, health management, design and battery life. The GT 7 Pro features a nano-tech ceramic bezel and titanium alloy frame, while the series adds new capabilities such as wrist-based turn and G-Force detection, ski mapping across more than 3,000 resorts, advanced cycling features and AI-powered insights. The company is also bringing the HUAWEI WATCH 6 Series back to Europe, with AI-driven workout analysis, independent calling, navigation and payment capabilities, alongside enhanced health and wellness features.
The company says its digital-health ecosystem now includes partnerships with more than 160 healthcare institutions globally and more than 10 research centres, including three sports and health science laboratories.
Zhou Hong, President of Huawei Research Institute, Europe, said the broader value of wearables lies in their ability to gather health information outside traditional settings. “Wearable devices enable fast, convenient and reliable multimodal measurements anytime and anywhere, providing actionable insights to personalize interventions and support more effective behaviour management. That is why the health sector is so promising: the potential for discovery is enormous, and the need has never been greater.”
Huawei is not just adding another health feature to a smartwatch. It is attempting to build an ecosystem spanning sensors, devices, software, research platforms and healthcare partnerships.
Significantly, Huawei also announced the launch of HUAWEI Mate XT 2 in Guangzhou, China. First smartphone to feature the LogicFolding Tau chip, Huawei Mate XT 2 comes with the new Kirin 9050 Pro chip and several upgrades in durability, AI, privacy and photography. More importantly, the device also brings health features including ECG analysis.
As basic fitness tracking becomes increasingly commoditised, differentiation is likely to come from the quality of health measurements, validation, longitudinal data and the ability to turn that information into useful insights. Huawei is taking a lead in this by developing a range of devices that are designed not just to give reliable measurements but also to contribute to the wider health ecosystem.
Algeria’s Ministry of Post and Telecommunications has announced the launch of plans to bring telecommunications services to 3,000 areas across the country, with a view to strengthening national coverage.
The ministry this week launched a call for tenders. Regulator ARPCE calls this operation, « the largest of its kind in this field », and states that it will benefit 3,000 localities throughout the country’s wilayas (administrative divisions), especially areas with low population density (fewer than 2,000 inhabitants).
This is to be a state-financed operation and part of broader efforts to expand telecom access and promote digital inclusion, particularly in rural and hard-to-reach areas. Telecom service providers ae being invited to submit their offers to ensure coverage and provide services in these areas to help reduce the digital divide. The country’s service providers include Djezzy, Ooredoo and Mobilis. Whoever wins the tender will be asked to deliver services within a period not exceeding 18 months.
News service Ecofin points out that the initiative comes as authorities complete a similar but smaller mobile coverage programme designed to bring 4G coverage to 1,400 communities across the country’s 58 wilayas and expand access to mobile phone and Internet services.
It appears that Algeria already has near-universal mobile network coverage. According to data from the International Telecommunication Union (ITU), 2G covered the entire population in 2025, while both 3G and 4G networks reached 99.1%. 5G remains in its early stages.
However, reliance on telecoms is, it seems, growing. Ecofin says more public and private services are moving online, including administrative procedures, financial services, education, health and commerce.
We caught up with Steven Offerein, VP of Product, Device Intelligence and Protection Services at CUJO AI, to discuss changes to the EU’s cybersecurity rules for connected products and what that will mean for operators
From 11 September, the first major obligations under the EU’s new cybersecurity rules for connected products take effect, with mandatory reporting of actively exploited vulnerabilities and severe security incidents. While much of that responsibility falls on manufacturers, operators have good reason to pay attention: they supply and manage millions of gateways and other connected products, and in some cases may themselves fall within the CRA’s definition of a manufacturer.
The regulation may put manufacturers on the clock, but operators are often the ones left dealing with the consequences on the network. That raises a bigger question: as Europe redraws the rules around connected-device security, where does the manufacturer’s responsibility end, and the operator’s begin?
Steven Offerein looks at what happens next, from identifying affected devices to protecting customers when a patch is no longer an option.
On paper, the CRA is a manufacturer’s law. Why is it an operator’s problem?
Two reasons. The first is that operators are not always just customers under the CRA; they can also be subject to it. If you put your brand on a gateway or substantially modify a product in a way that affects its cybersecurity, you may find yourself in the manufacturer’s seat, with the manufacturer’s obligations. Plenty of operators haven’t worked out yet which side of that line their CPE portfolio sits on.
The second is scale. An operator with tens of millions of gateways in the field is, in practical terms, one of the parties closest to the problem when a vulnerability is being actively exploited. The manufacturer may have the reporting obligation, but the exploit traffic runs across the operator’s network and into its customers’ homes. The CRA formalises the reporting, but it doesn’t change who must deal with the consequences.
Most of the industry is treating the CRA as a December 2027 problem. What are they missing?
The date. Most of the attention has gone to the full conformity requirements, CE marking, essential security requirements and support periods, which apply from December 2027. But the reporting obligations arrive first, on 11 September 2026, and crucially they apply to products already on the market, not just new ones.
The other misconception is that this is purely a paperwork exercise. A 24-hour reporting window puts pressure on the entire vulnerability-response process. For operators that also qualify as manufacturers, that means having the processes in place to establish what has happened and respond quickly. More broadly, operators need to understand whether a disclosed vulnerability affects devices across their installed base.
So, what concretely changes on 11 September, and who is actually on the clock?
For anyone who qualifies as a manufacturer, the mechanics are specific: an early warning within 24 hours of becoming aware of an actively exploited vulnerability or a severe incident, a fuller notification within 72 hours, and a final report once the issue is resolved. Reports go through the CRA’s single reporting platform, with the relevant national CSIRT and ENISA involved in the process.
For operators that don’t hold the manufacturer’s role, the change is more indirect but still important. Their vendors will have new legal reporting obligations when they become aware of active exploitation or severe incidents affecting their products. That should mean information about problems in the installed base moves more quickly.
But knowing a vulnerability exists is only step one. Knowing which subscribers actually have the affected device, whether it can be updated, and what you’re going to do about it is a different challenge.
You talk a lot about visibility. How can an operator managing 20 million gateways not know what’s connected to its own network?
Because the gateway fleet and the device population behind it are two completely different problems. Operators know what they’ve shipped. What’s much harder is maintaining a reliable, current view of what is actually connected behind those gateways — not what’s in a procurement database, but what’s present in customers’ homes.
Behind 20 million gateways, you’ll typically find several hundred million connected devices. Those devices arrive without registration, identify themselves inconsistently or not at all, and the mix changes every day.
Real visibility means identifying those devices by type, model and, where possible, software or firmware version, continuously and at population scale. When a vulnerability disclosure lands, the difference is being able to say, “We have 340,000 potentially affected devices across these markets,” rather than, “We genuinely don’t know.”
A vulnerability gets disclosed. Why is “which homes have this device?” now such an important question?
Detection without identification doesn’t lead to an actionable response. If you know an exploit is circulating but can’t say which homes have the affected device, you either treat every subscriber as potentially affected or risk missing the ones that are.
Identification turns a CVE from an abstract industry problem into a sized, addressable operational task. I think the ability to map a disclosure to an affected device population quickly will increasingly become a baseline operator capability, much like outage mapping is today.
Say that an operator knows exactly which devices are vulnerable. Then what?
It depends entirely on the device. For CPE the operator controls, the path is relatively clear: prioritise and push the firmware update, then use the management infrastructure to track uptake. For third-party devices in the home that still have vendor support, the operator’s role is more about awareness — helping customers understand what’s affected and what action they can take. Then there’s the third category, which is the uncomfortable one: devices that are vulnerable and will never receive a fix. That’s where the conversation shifts from remediation to mitigation.
The CRA is designed to ensure vulnerabilities are handled. What about the millions of existing devices that may never receive another update?
This is the reality nobody likes to talk about. Walk into an average European home, and you’ll find devices whose manufacturers no longer exist, cheap IoT products that never had a meaningful update mechanism in the first place, and perfectly functional equipment that has simply aged out of support. The customer often has no idea, and frankly no reason to know. The camera still streams, the plug still switches.
The CRA should improve this over time by requiring manufacturers to define support periods and establish proper vulnerability-handling processes for products covered by the new requirements. But it doesn’t make the existing population of unsupported devices disappear. Those products could remain in homes for years, and for many of them, “install the patch” simply isn’t an option. Something else has to mitigate the risk.
Is it really the operator’s job to protect a consumer’s abandoned smart camera?
Operators are in a unique position to help. If the device can no longer protect itself and the manufacturer is no longer providing updates, the network may be one of the few remaining places where protections can be applied.
The gateway sits in a particularly useful position because traffic to and from that device passes through it. Network-level security can block known malicious traffic before it reaches a vulnerable device, detect unusual behavior that may indicate compromise, and help contain compromised devices so they can’t threaten other devices in the home or be recruited into a botnet. None of that requires the vulnerable device to cooperate, which is precisely the point.
The CRA focuses on responsibility for the security of the product. Network-level security can provide another layer of protection, particularly where product-level protections are no longer available.
Will the CRA genuinely change how operators buy and manage CPE, or will price still win every RFP?
It should. Support periods, vulnerability handling, and update capability used to be secondary criteria in many RFPs, behind factors such as price and performance. The CRA gives those considerations much more weight.
It also forces more honesty around lifecycle management. Operators have historically been comfortable letting CPE sit in the field for a long time, because replacing hardware at scale is expensive. When a gateway carries a defined support period and vulnerabilities have to be handled throughout that period, end of support becomes a much more visible event. Operators have to plan for it: extend support contractually, replace the unit, or understand how the remaining risk will be mitigated.
Some argue that the CRA will force operators to pull CPE from the field sooner. Do you buy that?
Not necessarily. I think the more interesting outcome could be longer, better-supported lifecycles.
The wasteful pattern today isn’t always hardware living too long; it’s hardware being abandoned by software long before the silicon is done. A gateway can remain physically capable of providing service for years after active software support has declined.
The CRA puts more commercial and legal structure around support periods. That gives operators a reason to demand longer commitments upfront and gives vendors a way to account for those commitments commercially.
There’s also a sustainability angle. Replacing millions of units before the hardware itself needs replacing carries both an environmental and financial cost. The better outcome is hardware that’s properly supported for longer, alongside additional protections where updates are no longer available.
What are operators still failing to ask their hardware and software vendors?
I’d start with a few basic questions. Who is the manufacturer of record for this product under the CRA — you or us — and is that written down? What is the committed support period, and what exactly does “support” include?
Then, there are operational questions. Can you provide and maintain a software bill of materials? What is your coordinated vulnerability disclosure process? How quickly will we hear from you when something is being actively exploited? And are the reporting responsibilities between us clear enough that nobody is debating ownership when the clock starts?
A few years ago, some of those questions might have seemed overly cautious. Today, they need to be part of the conversation.
Every vendor now claims to “solve” CRA compliance. What can device intelligence honestly do, and what can’t it?
Let me be clear about the limits first: no platform makes you CRA compliant. Compliance involves processes, documentation, conformity assessment and legal accountability, and that responsibility belongs to the organization.
Where device intelligence can help is at the operational layer underneath. It can give operators a more accurate picture of what’s actually connected across the subscriber base, allowing a vulnerability disclosure to be mapped to a real device population much more quickly.
Combined with network security capabilities, visibility can also help operators understand suspicious behavior and apply protections to vulnerable or compromised devices — including devices that may never receive another update.
The CRA defines the responsibilities. Device intelligence can help operators build the visibility needed to respond at the scale of a broadband network.
An operator can’t fix everything before the deadline. What comes first?
Three things.
First, settle the role question. Go through your CPE and software portfolio and determine, product by product, whether you’re a manufacturer, importer or distributor under the CRA. Everything else depends on that answer, and it’s legal exercise, not a technical one.
Second, build the reporting process now. If any part of your portfolio puts you in the manufacturer’s seat, you need a rehearsed path from “we’ve become aware” to an early warning within the required timeframe. That means clear ownership, internal escalation, and an on-call process that exists before you need it.
Third, invest in visibility of the installed base — both the CPE fleet and the device population behind it. When a new vulnerability emerges, operators need to be able to establish what is affected, where it is, and what action is possible. Operators that can answer those questions quickly will be in a much stronger position to respond. Those that can’t may find every new disclosure becomes a fire drill.
Steven Offerein is VP of Product, Device Intelligence and Protection Services at CUJO AI, the market leader in device intelligence, network intelligence, and cybersecurity solutions for network operators, protecting more than 60 million households worldwide. He has over 15 years of experience in cybersecurity, telecommunications, and product leadership. Before joining CUJO AI in 2025, Steven held senior roles at F-Secure and TalkTalk, developing security solutions and connected-home products for international markets.
Data centre company HyperVault, a subsidiary of Indian technology group Tata Consultancy Services (TCS), says it has secured 264 acres of land to develop a large-scale AI data centre campus of up to 1GW capacity in Hyderabad.
HyperVault says the Hyderabad AI data centre campus will be purpose-built to serve the needs of frontier AI companies and hyperscalers, enabling high-density GPU deployments for AI training, inference and advanced computing workloads.
The precise timeline for the development has not yet been revealed. However, the company says the development of the data centre campus will be executed in a phased manner, in line with customer demand and technology requirements.
It adds that at full build-out, the campus is expected to rank among the most advanced and largest AI infrastructure campuses in India. The campus will also leverage green energy and water-neutral design principles as part of the build-out.
Beyond the campus, the project is expected to catalyse India’s AI infrastructure ecosystem across power, cooling, networking, construction, engineering and operations. The project will generate several thousand direct and indirect jobs in the region. HyperVault and its partners are expected to invest up to Rs 70,000 crore (about US$7.4 billion) to build and manage this infrastructure.
K Krithivasan, CEO & MD, TCS, says” “HyperVault advances TCS’ infrastructure-to-intelligence strategy by bringing together AI-ready infrastructure with our cloud, engineering, enterprise transformation and AI capabilities. Hyderabad offers the scale, talent and ecosystem to serve global customers.”
We use cookies to personalise content and ads, to provide social media features and to analyse our traffic. We also share information about your use of our site with our social media, advertising and analytics partners. View more
Cookies settings
Accept
Privacy & Cookie policy
Privacy & Cookies policy
Cookies list
Cookie name
Active
Conditions légales
Introduction et qui nous sommes
118812.fr met en relation des spécialistes du monde entier par le biais d'événements, de renseignements et d'éditions savantes. Nous sommes une société du FTSE 100 et notre réseau de marques internationalement respectées aide les gens à travailler plus intelligemment, à prendre de meilleures décisions et à se développer sur des milliers de marchés spécialisés. Les données et les informations sont au cœur des activités de 118812.fr, et nous prenons au sérieux les questions de confidentialité des données. Nous respectons nos relations avec les clients, les visiteurs, les sponsors, les exposants, les fournisseurs et les collègues, ainsi que la confiance qu'ils nous accordent pour la conservation de leurs données personnelles.
Contrôleurs de données de 118812.fr
Cette politique de confidentialité explique comment les membres du groupe 118812.fr collectent, utilisent et protègent les informations personnelles à travers nos marques. Les références à "nous", "notre" ou "nos" renvoient au contrôleur 118812.fr concerné qui traite vos informations personnelles.
118812.fr est structuré en cinq divisions opérationnelles :
Au sein de ces divisions, il existe des entreprises sectorielles et des marques de produits, d'événements et de services. En général, lorsque nous interagissons avec vous, c'est par le biais de l'une de ces marques. L'entité juridique du groupe 118812.fr responsable des données personnelles (désignée comme le contrôleur des données dans l'UE et désignée comme le contrôleur 118812.fr dans la présente politique de confidentialité) sera l'entité indiquée sur les formulaires de réservation, les formulaires Web et les contrats ou les factures. Différentes entités juridiques de 118812.fr sont responsables de différents événements et produits. Pour mettre à jour vos informations personnelles ou vos préférences en matière de marketing, contactez les équipes de marketing de nos divisions énumérées ci-dessous. Pour toute question ou plainte concernant la confidentialité des données, vous pouvez vous adresser à l'équipe 118812.fr Privacy via notre formulaire en ligne.
Couverture internationale et variations
118812.fr opère dans plus de 20 pays, qui ont chacun des lois différentes sur la protection des données. La présente politique de confidentialité s'applique à toutes les activités de 118812.fr dans le monde, sauf dans la mesure où il existe une exigence spécifique à un pays qui la complète, comme indiqué dans le menu de gauche.
Ce que nous recueillons
Cette section vous indique quelles informations personnelles nous pouvons recueillir lorsque vous utilisez nos produits et services, et quelles autres informations personnelles nous pouvons recevoir d'autres sources. Dans la présente politique de confidentialité, les informations personnelles désignent les types de 118812.frtions personnelles qui peuvent être collectées et utilisées, notamment : Les coordonnées, telles que le nom, l'adresse électronique, l'adresse postale et le numéro de téléphone.Informations sur l'éducation, la nationalité et la professionles noms d'utilisateur et les mots de passeCommentaires, réactions, messages et autres contenus soumis, y compris les informations relatives aux enquêtes.Intérêts et préférences de communication, y compris les autorisations de marketing, le cas échéant.Informations de localisation, telles que celles fournies par une application mobileInformations de vérification de l'identité, telles que les détails du passeport, afin de se conformer aux obligations légales dans certains pays et de fournir des lettres d'invitation de visa, le cas échéant.Informations sur l'utilisation du site web et des communications, telles que la correspondance et les détails de votre utilisation de notre site web et de nos services obtenus par le biais de cookies ou d'autres technologies de suivi.
Ces informations personnelles concernent les catégories de personnes suivantes :
Prospects, contacts clients, abonnés et utilisateurs en ce qui concerne nos services et produits ;Visiteurs, sponsors, exposants et conférenciers lors de nos événements ;Les professionnels figurant dans les produits numériques et imprimés, tels que les détails des cadres supérieurs mis à disposition par les produits de renseignement, les recherches et les publications.les auteurs, éditeurs et réviseurs de nos publications.les contacts de nos prestataires de services et partenaires commerciaux.Informations personnelles sensibles