Toyota completes Phase 1 of Mount Fuji smart city construction


News

At CES 2025, Toyota Motor Corporation announced the completion of Phase 1 construction of Toyota Woven City (“Woven City”), its self-made smart city at the base of Mount Fuji.

The Japanese automaker giant has labelled the city as a “test course for mobility” and plans to launch Phase 1 for late 2025.

Speaking at the CES confrence, Akio Toyoda, Toyota’s Chairman of the Board of Directors (Representative Director), detailed his vision for the city: 

“From personal mobility devices, like a wheelchair race car…to drones that safely escort you home at night, to interactive pet robots that provide support and companionship for the elderly, to flying cars…”

[embedded content]

At the official launch of Woven City, approximately 100 residents―primarily Toyota and WbyT staff and their families―are expected to participate in co-creation activities as the first residents. Plans to welcome the general public are in place for 2026.

The Woven City concept was first unveiled in 2020, where it was described as a “living laboratory”.

Woven City is ideated to be where “Inventors” can develop, test, and validate innovative products and services. These inventors include Toyota and Toyota Group companies, such as WbyT, as well as external companies, startups, and individual entrepreneurs.

This article was written by Grace Dawes, Editor of movemnt.net

Also in the news:
VEON and Starlink to launch Direct-to-Cell Satellite connectivity in Ukraine
Swisscom completes acquisition of Vodafone Italia
Equinix to buy BT’s Irish data centre business for €59m

2024 was worst year on record for commercial cyberattacks

For the first time since 2021, the final quarter of 2024 was not the most prolific period of the year for cyberattacks. The attack rate peaked at 2,192 per day in the third quarter of 2024 before declining to 2,063 per day in Q4. Despite this reduction, the final three months of 2024 were only the third quarter on record when the average number of cyberattacks encountered by UK businesses exceeded 2,000 a day.

Previously, 2023 was the worst year on record for cyberattacks on UK businesses, when companies encountered an average of 720,252 malicious attempts to breach their systems each. Before 2024, the average number of attacks in a single quarter had only exceeded 2,000 in Q4 2023.

Remote IoT devices attract most cyberattacks 

Hackers attacked remotely controlled devices connected to the Internet of Things most frequently in 2024. Business firewalls encountered more than 161 daily attacks targeting applications such as building control systems, security cameras, networked printers, remote monitoring, and industrial automation systems. 

Web applications, remote desktop software, and company databases were also frequently targeted, with businesses typically attracting more than 20 individual attacks daily for each of these systems in 2024.

Beaming tracks a quarter of hackers to locations in China

Beaming’s analysts identified over a million IP addresses being used to launch cyberattacks on UK businesses in 2024 and traced almost a quarter (241,019) of them to locations in China. Beaming also identified significant and increasing volumes of cyberattacks that appeared to come from areas inside India (87,144 attacking IP addresses) and the USA (81,112) in 2024.

Sonia Blizzard, Managing Director of Beaming, said: “The rise of automated cyberattacks means the internet has never been more dangerous, and we expect it will become even more so as hackers use AI. The good news is that we are not seeing record numbers of companies crippled by hackers because businesses have got better at protecting themselves and ISPs such as Beaming are working hard to prevent malicious activity at a network level.”

Demand for specialised cyber services in the UK continues to soar


Press Release

A ten-fold increase in customers in the space of a year has led Red Helix, a market leader in cyber security and network performance, to invest £1million in expanding the capacity of its UK-based 24/7 security operations centre (SOC), increasing headcount by 150%. The company expects its SOC team to grow further in 2025, as demand for its specialised cyber services continues to soar.

Despite the global cyber skills shortage, Red Helix has been successful in recruiting and retaining SOC analysts who understand real-world security in small and medium-sized companies. The investment has been dedicated to creating innovative workspaces to support this talent, building a first-class team, and deploying an integrated suite of tools to ensure Red Helix can continue delivering industry-leading cyber security services tailored to the unique needs of SMEs.

Since its launch, Red Helix’s round-the-clock SOC coverage has brought enterprise-level security to the small and medium-sized businesses that often lack the in-house skills or resources to evaluate, integrate, and manage the security platforms they need.

As Red Helix CEO, Marion Stewart explained, “Our mission is to bridge the gap between the needs of small to medium businesses and the high-degree of complexity in security solutions they need – which are usually only accessible to larger enterprises.”

“By investing in our SOC,” she continued, “we’re able to protect more UK businesses from ever-evolving cyber threats. For many SMEs, one breach could jeopardise the entire company. Moreover, as small suppliers can be targeted to reach larger enterprises, there’s increased pressure on all supply chain members to uphold strong security. Each member of our SOC team understands the critical role our services play in protecting businesses from cyber disruptions. They are dedicated to providing proactive, reliable security, giving companies confidence that they’re in safe hands.”

The SOC, based at Red Helix HQ in Buckinghamshire, combines best-of-breed technologies with human expertise and provides a service that protects companies’ users, devices, networks, data, and applications in cloud, on-premise and hybrid environments. Through the company’s innovative pod structure, its team of analysts gain an in-depth understanding of each client’s systems and behavioural patterns. They then configure tailored triggers to detect anomalies and security breaches, taking swift and appropriate action as required.

“Taylor Howse, Cyber Security Analyst at Red Helix, said, “We equip our skilled SOC team with top-tier tools to deliver exceptional service. In the ever-evolving cyber world, every day brings new challenges, so staying ahead of threats requires constant readiness. Our structured training ensures we’re prepared. Each day, I analyse security logs and investigate anomalies – not just because I love the work, but also because Red Helix plays a vital role in safeguarding our customers’ environments, and being a part of that is hugely rewarding.”

The expansion of the SOC team comes as Red Helix continues its growth trajectory, having recently announced the appointed former British Army officer, Tom Exelby, as its new Head of Cyber Security. The company was also named as one of the top 40 cyber security companies in the UK and Europe 2024 by TechRound.

US court blocks reinstatement of net neutrality


News

The court of appeal ruled on Thursday that the Federal Communications Commission (FCC) does not have the legal authority to reinstate the rules

This week has seen a US appeals court strike a major blow to the Biden administration’s aspirations of restoring net neutrality, ruling that the FCC does not have the power to enforce such regulations.

Net neutrality is the concept that all internet users and internet traffic should be treated equally by service providers. This paradigm means that providers may not block, slow down, or charge different rates for specific online content. Championed by the Democrats for over a decade and formally introduced as a ruleset by the Obama administration, net neutrality was then rescinded in 2018 during the Trump presidency.

As a paradigm, net neutrality has been highly political since its inception, with left-leaning Democrats arguing that net neutrality principles are necessary for a fair and open internet, while right-leaning Republicans see it as heavy-handed and unnecessary regulation of the free market.

Joe Biden made the reinstatement of net neutrality a focal point of his election campaign, issuing an executive order encouraging the FCC to reinstate the rules in 2021.

Now, following this new ruling from a US appeals court, it seems that net neutrality’s return is unlikely.

The courts new ruling hinges on a new precedent set by the US supreme court case (the ‘Loper Bright’ case) last summer. This case saw a previous precedent – known as the 1984 Chevron doctrine – overturned, ruling that only the judiciary should have the power to interpret the law in ambiguous cases, rather than federal agencies like the FCC.

Since previous net neutrality rulings by the FCC rested on their interpretation of ambiguous regulatory law via the Chevron doctrine, these arguments are no longer valid.

“Applying Loper Bright means we can end the FCC’s vacillations,” read the court ruling.

In reaction to the ruling, FCC chair Jessica Rosenworcel argued that it was now necessary for Congress to enshrine net neutrality principles into federal law.

“Consumers across the country have told us again and again that they want an internet that is fast, open and fair. With this decision it is clear that Congress now needs to heed their call, take up the charge for net neutrality and put open internet principles in federal law,” she said.

However, with Congress majority controlled by anti-net neutrality Republicans, it seems unlikely that this call to action will bear fruit – at least during the incoming Trump administration.

Republican FCC Commissioner Brendan Carr, on the other hand, was much more positive about the ruling, describing net neutrality regulations as the Biden government’s “internet power grab”.

Brendan Carr is set to take over as FCC chair under the incoming Trump administration.

Keep up to date with all the latest telecoms news from around the world with the Total Telecom newsletter

Also in the news:
VEON and Starlink to launch Direct-to-Cell Satellite connectivity in Ukraine
Swisscom completes acquisition of Vodafone Italia
Equinix to buy BT’s Irish data centre business for €59m

Zegona and MasOrange partner to create Spain’s largest fibre network 


News 

The deal follows Zegona’s €5 billion purchase of Vodafone Spain last June 

Zegona Communications has announced that Vodafone Spain and MasOrange will form a new fibre network joint venture, dubbed FibreCo. 

FibreCo will combine the two companies’  fibre-to-the-home (FTTH) networks, reaching roughly 12.2 million premises across Spain. This, the partners say, will create the largest FTTH network in Europe. 

FibreCo will use existing infrastructure, with nearly 40% of the combined FTTH network already in use  by 4.5 million customers. It plans to deploy the latest technologies, such as XGS-PON, to improve service quality. Vodafone Spain will use FibreCo to deliver services to both retail and wholesale customers. 

FibreCo is expected to generate approximately €480 million in annual EBITDA within three years.  

A third-party investor is also being sought to join the venture, with the proposition already reportedly receiving strong interest. Under the proposed structure, MasOrange will retain 50% ownership, Zegona will hold 10%, and the third-party investor will take a 40% stake. 

“Entering this FibreCo partnership with MasOrange, alongside our recently announced agreements with Telefonica, transforms Vodafone Spain’s fixed line strategy. The combination will give guaranteed access to a future-proof all fibre national network with attractive economic terms and will enable substantial cost savings across the business. Monetising these two FibreCos is expected to deliver very significant Zegona proceeds, generating the ability to reduce leverage and provide a return of capital to shareholders,” said Eamonn O’Hare, Chairman and CEO of Zegona in a press release. 

The initiative follows Zegona’s recent agreement with Telefónica to establish another fibre network in Spain and renew wholesale access terms. Combined, these projects represent a significant overhaul of Vodafone Spain’s fixed-line strategy, enabling full FTTH coverage across the country and achieving cost efficiencies.  

The deal is subject to regulatory approval and is expected to close by mid-2025, alongside the onboarding of a third-party investor. 

Keep up to date with the latest international telecoms news by subscribing to the Total Telecom newsletter 

Also in the news:
Equinix to buy BT’s Irish data centre business for €59m
Part 2: More US broadband predictions as we approach 2025
World’s first 5G-A region in Mobile AI Era launched 

NTT Docomo hit by DDoS attack


News

The distributed denial-of-service (DDoS) attack caused a website failure and service disruption for around 12 hours

Today, Japan’s largest mobile operator, NTT Docomo, has revealed it has suffered a cyberattack, impacting a number of services.

The DDoS attack reportedly resulted in a system glitch at 5:27am, which disrupted access to several services – such as the company website and the company’s ‘goo’ portal – for almost 12 hours.

Mobile and other communication services were notably unaffected, though customers reported difficulty accessing the company’s ‘d payment’ mobile money service.

Cyberattacks on telecoms operators have been increasing in potency in recent years. While this attack on Docomo was relatively benign, more sophisticated attacks can put the data from millions of customers at risk. Last year, for example, a data breach at AT&T saw data from 73 million customers leaked on the dark web.

Cyberattacks are typically motivated by financial gain, primarily via blackmailing the victim or the sale of the stolen data. However, as the world becomes increasingly politically unstable we are seeing activity by state-supported hacker groups focus more on surveillance and sabotage for geopolitical ends.

Indeed, this was seemingly the motivation for a string of attacks reported at the end of last year, in which the Chinese hacker group Salt Typhoon was linked to a series of cyberattacks on the US telecoms sector. These attacks compromised data from at least nine major service providers, including AT&T, Verizon, and T-Mobile.

US Senate Intelligence Committee Chairman Mark Warner dubbed the breach “the worst telecom hack in our nation’s history – by far.”

Keep up to date with all the latest telecoms news from around the world with the Total Telecom newsletter

Also in the news:
VEON and Starlink to launch Direct-to-Cell Satellite connectivity in Ukraine
Swisscom completes acquisition of Vodafone Italia
Equinix to buy BT’s Irish data centre business for €59m

VEON and Starlink to launch Direct-to-Cell Satellite connectivity in Ukraine  


News 

The connectivity could prove vital in areas where infrastructure is destroyed by Russian military activity 

Telecoms group VEON has announced a new partnership with Starlink, a division of SpaceX, to bring direct-to-cell satellite connectivity to Ukraine.  

The deal will see Kyivstar, VEON’s Ukrainian subsidiary, offer these satellite-based connectivity services to its customers across the country. 

The deal will see Ukraine become one of the first countries to benefit from Starlink’s direct-to-cell services, with T-Mobile in the US the only other operator that has agreed to roll out the technology so far.  

Service activation in Ukraine is expected in the fourth quarter of 2025 and will include SMS and over-the-top (OTT) messaging functionality. Service offerings will expand to include voice and data services in future phases. 

Global satellite constellation Starlink is currently operational in roughly 118countries worldwide, where it aims to serve customers in regions where traditional internet infrastructure is limited. Its technology has already played a significant role in connecting areas affected by natural disasters, conflict, and other infrastructure challenges. 

All of these deployments, however, currently require the use of a Starlink terminal dish. Direct-to-cell capabilities, on the other hand, will allow customers to use the satellite connectivity without any deploying any additional equipment.  

These capabilities are limited the latest Starlink satellite models, of which SpaceX has launched over 100 in the past year. 

For Ukraine, this satellite connectivity could provide customers with an invaluable emergency resource, allowing them to stay connected even when terrestrial infrastructure has been destroyed by Russian military action. 

“Kyivstar has done a tremendous job in investing in Ukraine’s 4G connectivity, expanding coverage to remote areas and increasing the energy resilience of its network. Today’s announcement helps us take our commitment to Ukraine’s connectivity to the next level, exponentially amplifying the resilience of our services with satellite connectivity,” said Kaan Terzioglu, CEO of VEON Group in a press release. 

Kyivstar CEO Oleksandr Komarov emphasised the importance of the collaboration in ensuring continuous communication for customers in Ukraine, especially during ongoing challenges.  

“Kyivstar has been the backbone of Ukraine’s resilience throughout the war, and we are committed to leaving no stone unturned to keep Ukraine connected. Our collaboration with Starlink is a game-changer in our journey towards achieving our ‘LTE everywhere’ ambition,” he said. 

VEON, which has invested over $10 billion in Ukraine since 2013, has committed an additional $1 billion for the country’s recovery and reconstruction between 2023 and 2027. The company was named the top international investor in Ukraine for 2022 and 2023 by Forbes Ukraine and NV Ukraine. 

“Working with Starlink allows us to extend connectivity to underserved areas, supporting our broader mission to provide reliable services in emerging markets,” said Augie K Fabela II, Chairman and Founder of VEON.  

At the World Communication Awards held last month in London, VEON Kyivstar won the Crisis Response Award. 

Keep up to date with the latest international telecoms news by subscribing to the Total Telecom newsletter 

Also in the news:
Equinix to buy BT’s Irish data centre business for €59m
Part 2: More US broadband predictions as we approach 2025
World’s first 5G-A region in Mobile AI Era launched 

For two consecutive years, Huawei has been recognized among notable vendors in the zero trust edge field


Viewpoint

[Beijing, China, December 16, 2024] Huawei announced today that Forrester, an international authoritative organization, recently released The Zero Trust Edge Solutions Landscape, Q4 2024 (hereinafter referred to as the “Report”), which provides an overview of zero trust edge solutions (secure access service edge or SASE technologies like SD-WAN, ZTNA, SWG) of 25 vendors. This report provides an authoritative definition and overview of the zero trust edge market. Huawei has been named among notable vendors for two consecutive years.

The report analyzes the business value of SASE and covers the market maturity, technologies, and application scenarios of SASE solutions provided by different vendors. The report allows readers to identify potential partners who are the right fit for their organizations to implement a zero trust edge security model.

Huawei Xinghe Intelligent SASE Solution Building an Intelligent Security Protection System for Enterprises

In an increasingly complex network security environment, zero trust architecture has become the key for enterprises to ensure business continuity and cope with uncertainty. Huawei is one of the world’s first mainstream vendors to develop SASE solutions and has won multiple international security awards.

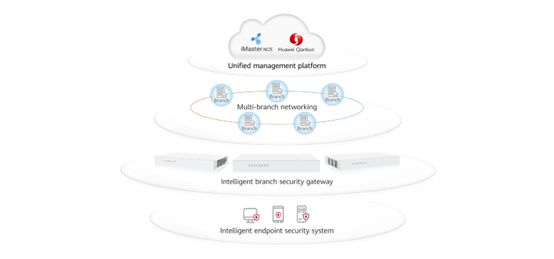
As more services are moved to clouds and more people are opting for hybrid working, enterprise branch networks face tremendous security challenges, and network security incidents occur one after another around the world. To address these challenges, Huawei’s Xinghe Intelligent SASE Solution provides a network security system featuring intelligent detection, collaboration, and integration by leveraging the cloud-network-edge-endpoint integrated architecture.

Intelligent detection: Huawei has made a breakthrough in the lightweight file emulator technology, which can unpack files in milliseconds. The lightweight Site AI model on the local gateway and 18 small AI models on the cloud are used to detect unknown threats, improving the detection rate to 95%.

Intelligent collaboration: Huawei’s HiSec Endpoint uses the innovative threat source tracing graph engine to accurately identify ransomware, achieving a 100% ransomware detection rate. With endpoint-network-storage collaboration, once ransomware is detected on one node, the information is synchronized to all network and storage devices for them to take protective measures.

Intelligent integration: Huawei’s unified security analysis platform has over 8000 inference rules and automatically delivers matching rules to automatically handle 99% of security events on the entire network in seconds. Branches do not need to assign dedicated maintenance personnel, improving operation efficiency by 100 times.

Huawei’s Xinghe Intelligent SASE Solution has been recognized by governments and enterprises in the finance, energy, transportation, education, healthcare, and other sectors around the world, helping them deploy zero trust architecture and build a next-generation security system for future business development.

Looking ahead, Huawei will continue to invest in the research and development of new technologies based on customer needs and help customers build a secure zero-trust network environment in the intelligent era.

Swisscom gets green light on €8bn Vodafone Italia Acquisition from Italian authorities 


News 

The acquisition was first announced back in March

Swisscom has officially received the green light for its acquisition of Vodafone Italia, following approval from both the Italian Competition Authority and the Ministry of Enterprises and Made in Italy (MIMIT). With regulatory hurdles cleared, Swisscom is now set to complete the deal by the first quarter of 2025. 

Last week, the Italian Competition Authority approved the transaction, accepting a series of behavioural commitments proposed by Swisscom. These include continuing to provide wholesale services to interested operators in line with Fastweb’s current practices, as well as sharing relevant information in any public tenders where Fastweb or Vodafone Italia is the supplier. An independent trustee will oversee the implementation of these commitments for the next three years. 

MIMIT granted unconditional approval for the deal on 19 December 2024, confirming the change of control over Vodafone Italia’s spectrum licenses. This followed positive assessments from the Italian Authority for Communications and the Italian Competition Authority. 

The merger of Fastweb and Vodafone Italia is expected to deliver substantial benefits to Italian consumers and businesses by combining their strong fixed and mobile infrastructures and expanding their range of services. The merger will create Italy’s second-largest fixed-line broadband operator behind Telecom Italia (TIM). This, they said, will create around €600 million in savings through increased scale and a more efficient cost structure. As part of the transaction, Vodafone will provide some service to Swisscom for the next five years. 

With regulatory approvals now in place, Swisscom anticipates that the acquisition will be finalised in early 2025, marking a new phase for the company in the Italian telecom market. 

Keep up to date with the latest international telecoms news by subscribing to the Total Telecom daily newsletter  

Also in the news:
Equinix to buy BT’s Irish data centre business for €59m
World’s first 5G-A region in Mobile AI Era launched
Part 1: Some US broadband industry predictions as we approach 2025

Part 2: More US broadband predictions as we approach 2025


Viewpoints

With the recent election behind us, there’s a noticeable shift in broadband industry sentiment.

By: Jason Malmquist, EVP, Head of Software and IT Services Business at CHR Solutions

To read the first part of this viewpoint series, click here.

Following the election, industry stakeholders are cautiously optimistic now about potential improvements in financing conditions, strategic network expansion, and the evolving competitive landscape. As we look to 2025, several key trends and challenges are emerging in the broadband industry; here are my top predictions.

1. Interest rates and cost of capital could stabilize

With political uncertainty temporarily out of the way, there’s hope for a more stable economic environment. We could see a reduction in interest rates and cost of capital. This would encourage providers to think more strategically about network investments. With financing a significant constraint over the past few years, any decrease in these costs could empower broadband companies to invest more confidently in their infrastructure.

2. Renewed focus on operational efficiency

During 2024, there were slower network buildouts and a shift toward operationalizing existing networks. Providers turned their attention to converting network passings to paying customers, a trend that’s likely to continue in 2025. While some new builds may resume, the frenetic pace of 2023 will not return. Instead, ISPs are looking at ways to optimize customer acquisition and improve ROI on existing networks. Expect to see targeted buildouts where demand is highest and a continued emphasis on streamlining operations.

3. Consolidation in the broadband space

A significant buzzword for 2025 is consolidation. Industry players and analysts are predicting that we’ll see more mergers and acquisitions this year because the convergence of high infrastructure costs and increased competition is driving many smaller providers to consider alliances or acquisitions as a way to stay competitive. Interestingly, even some co-ops—historically resistant to merging—are discussing consolidation. While co-op mergers may still be unlikely, this growing dialogue indicates that the landscape could shift as companies look for ways to scale efficiently and meet demand.

4. Starlink’s growing influence

In a surprising turn, Starlink’s influence on the broadband sector is growing. Providers are voicing more concern about the competitive threat posed by Starlink’s satellite internet service, especially with recent reports indicating that Starlink wasn’t significantly included in many broadband plans but may soon become a viable part of the ecosystem. While it’s not poised to replace traditional ISPs, Starlink’s coverage and appeal in underserved areas has made it a real competitor. In light of this, ISPs may need to reconsider their strategies, especially in rural regions where Starlink can offer a viable alternative.

5. Increased automation in service delivery

Indications are that during 2025, we will likely see a push toward greater automation in service delivery. From order processing to scheduling, the demand for seamless customer experiences is fueling automation across the board. Providers want to streamline the entire sales and onboarding process—from self-order systems to door-to-door sales tracking, shortening timelines and improving service reliability. The belief is that enhanced automation will enable ISPs to handle higher customer volumes more efficiently, driving both cost savings and customer satisfaction.

6. Rising cybersecurity threats for ISPs

Cybersecurity is no longer just a concern—it’s a critical risk that ISPs must address. Today’s cyber threats are sophisticated and coordinated, often executed by criminal organizations with ample resources and expertise. Smaller ISPs, especially in rural or underserved areas, are particularly vulnerable, as they may lack the IT infrastructure and security staff to defend against targeted attacks. These risks are significant: a security breach can lead to prolonged service outages, loss of customer data, and lasting damage to a company’s reputation. Therefore, ISPs need to prioritize cybersecurity, incorporating more advanced defenses and, ideally, dedicated teams or partnerships to mitigate these threats.
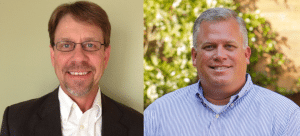
Left to right: Bob Bartz, VP of Engineering and Jason Malmquist, EVP, Head of Software and IT Services Business at CHR Solutions.

Left to right: Bob Bartz, VP of Engineering and Jason Malmquist, EVP, Head of Software and IT Services Business at CHR Solutions.

In summary …

The broadband industry will be defined by strategic expansions, a focus on efficiency, competitive pressure from satellite providers, and the urgent need for cybersecurity in 2025. It’s a complex environment, but with the right mix of innovation, automation, and strategic planning, providers can capitalize on opportunities and address the emerging challenges. By staying adaptable and vigilant, ISPs can navigate the evolving landscape and continue to deliver essential connectivity to their customers.

Click here to read Part 1: Some broadband industry predictions as we approach 2025 by Bob Bartz, VP of engineering at CHR Solutions.

To get content like this delivered to your inbox, subscribe to the Broadband Communities newsletter.